

Secureframe is the automated compliance platform built by compliance experts. We're transforming how businesses and MSPs manage security & compliance programs.
San Francisco, CA
- Tweets 1,713
- Following 150
- Followers 2,224
- Likes 561


Pinned Tweet

On average, DIB contractors spend $100K–$250K+ and 6–18 months on CMMC prep. Most can't afford that.
Today, we launched Secureframe Defense to help any organization go from zero to CMMC ready in 4–8 weeks.
Learn how: secureframe.com/blog/announc…

2
7
20
11,632
A fintech's AI assistant got talked into full account takeover over one conversation. Just one example of how AI is changing attack surfaces & what a pentest should cover. Breakdown by @softwaresecured: hubs.li/Q04yrthN0

40
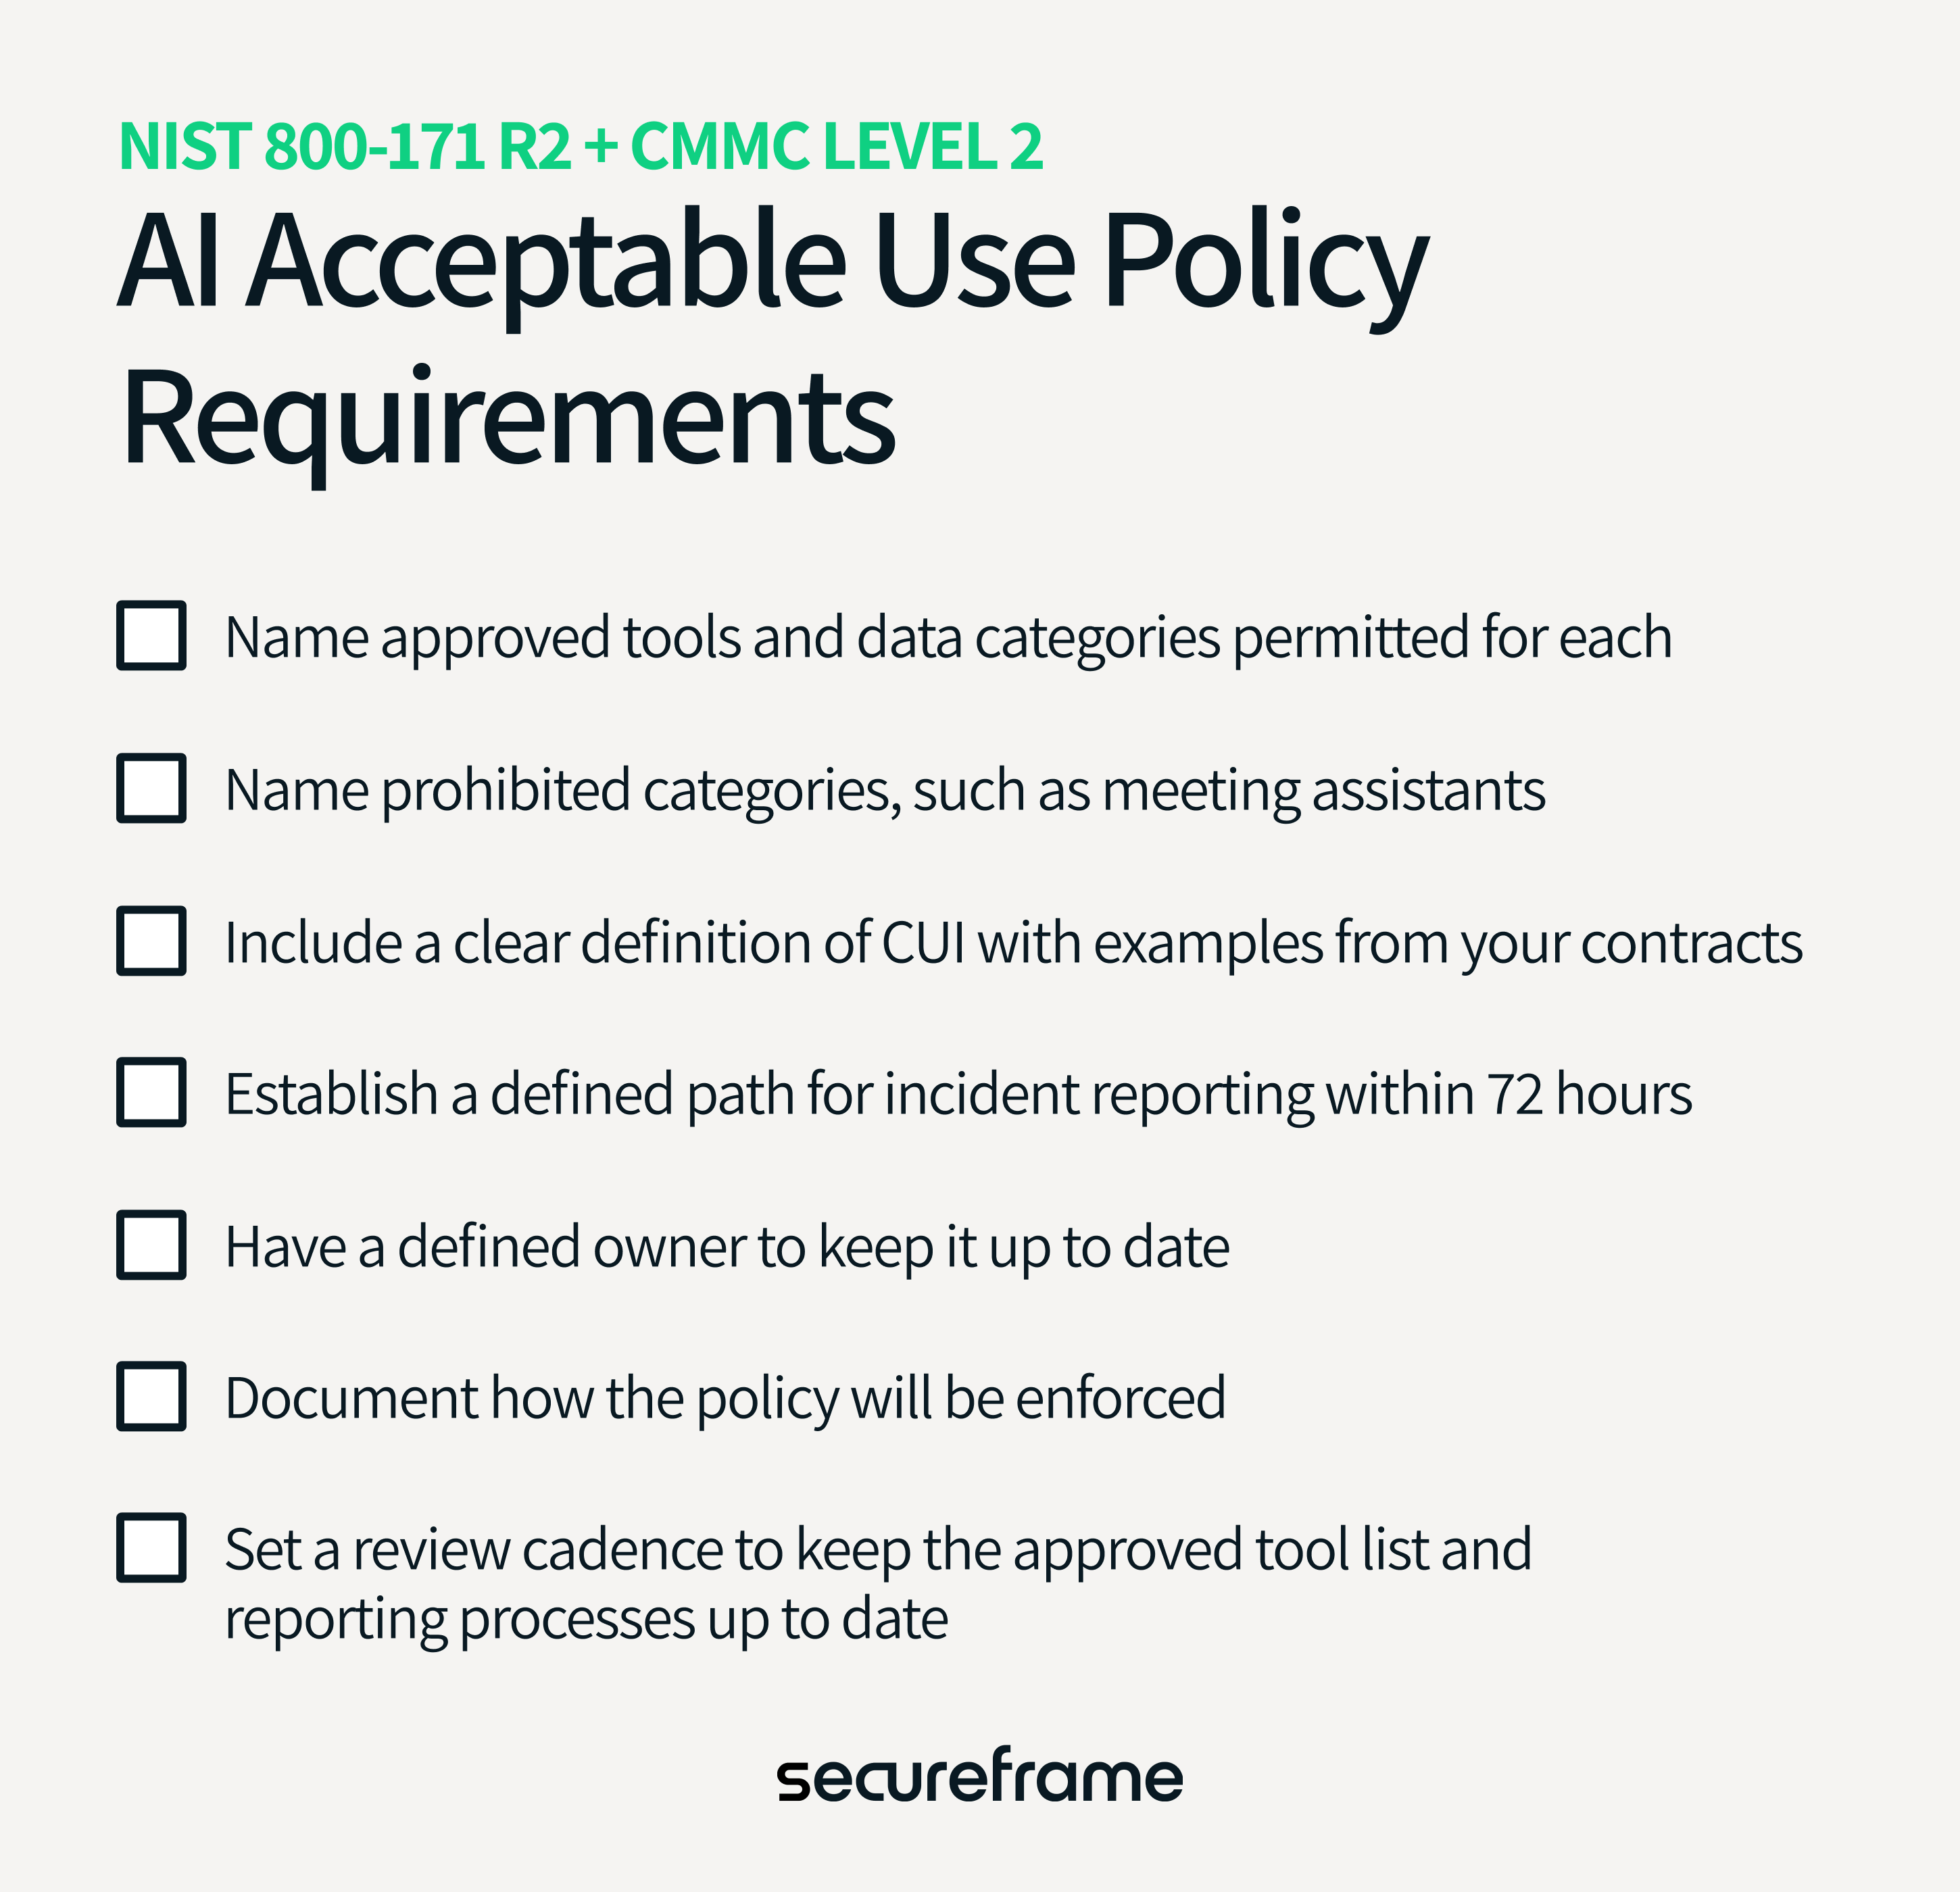
CISA, NSA, and FBI recently warned U.S. AI companies about industrial-scale model distillation. For DIB contractors the nearer issue is still CUI in a commercial tool. Requirements and templates: hubs.li/Q04y3jmt0
68
90% of AI-adopting leaders think longer retention improves models. Most frameworks still say keep it only as long as you need it, then dispose of it. Here's how to meet requirements while balancing business goals: hubs.li/Q04y3jl20

44
The FedRAMP 20x Class D (High) pilot RFC proposes one hard gate: a CR26-compliant Class C certification before Dec 1, 2026. So if Class D is on your roadmap, Class C is the work in front of you. Read our guide: hubs.li/Q04y3j590

40
CMMC reform feedback isn't just about who assesses you. Industry and the DoW CIO flagged inconsistent CUI designation as a major challenge reform is tackling. Guide to categories and where it shows up: hubs.li/Q04y2Sfl0
72
Some orgs are still running on NIST's outdated password rules. The latest guidelines formally recognize passkeys and expand phishing-resistant MFA, which DoW also named its #1 IT fundamental for DIB contractors. Read the guide: hubs.li/Q04xyZtC0

65
FedRAMP stops taking new Rev 5 applications June 11, 2027. 20x isn't a lighter Rev 5: 46 KSIs instead of a prescriptive ~400-control baseline, no agency sponsor, and a Class A path to the Marketplace via SOC 2 Type II. How they compare: hubs.li/Q04xyZvk0

80
CyberAB CEO Matt Travis said CMMC reform could potentially look to incorporate FedRAMP-style continuous monitoring. FedRAMP 20x runs this model on quarterly reports, not point-in-time re-assessments. How it works: hubs.li/Q04xz1Vv0

1
57
FAR overhaul batch 2 cleared OMB. Does it change CMMC? No: CMMC lives in 32 CFR 170 and DFARS, not the FAR. What it does change is when the text becomes permanent, and your window to object: hubs.li/Q04xyY2G0

1
93
Happening next week: our webinar with Software Secured on security testing in the era of AI.
Your AI assistants hold credentials and act on behalf of your team. Nothing in SOC 2, CMMC, or FedRAMP says go check what they can reach. Learn what you should do first.
Join us: hubs.li/Q04wzd8s0

2
64
The LiteLLM breach exposed 2,500+ orgs and 434K CI/CD pipelines in under 40 minutes, the largest AI supply chain attack this year. Discover other recent supply chain attacks and security fundamentals to prevent them: hubs.li/Q04wN4TD0

67
CUI protection has been a DoD requirement. The FAR Council's June proposal would extend it to civilian agency contractors government-wide. So we put 25+ free resources in one place to help you understand and build a CUI program: hubs.li/Q04wzvjT0

1
44
Small business primes working with the DoW fell 32% in a decade. SBA warns CMMC's costs could speed that decline. The DoW's CIO says the real fix is keeping manufacturers producing, not lowering the security bar. Worth a read this Labor Day: hubs.li/Q04wN48c0

60
Your AI assistant has access to your email, docs, and code. Can you say what it's actually permitted to do with them?
Secureframe + Software Secured go live Sept 17 at 1 PM ET to discuss challenges of scoping, testing & governing AI access.
Register: hubs.li/Q04wv9RS0

46
SPRS scores are increasing, but contractor confidence in their accuracy keeps dropping: 94% in 2024, 89% in 2025, 65% now. This matters more, not less. The Phase 2 pause didn’t change self-assessment or affirmation requirements: hubs.li/Q04w6vx60

63
Yesterday, Honeywell Aerospace settled False Claims Act allegations for $2M over NIST 800-171 failures that predate CMMC. Other enforcement mechanisms were used to catch it, and those are still in place during the pause. Learn more: hubs.li/Q04wmNTH0

86
The most frequently cited challenge in 11,000 pages of CMMC reform RFI feedback was not just cost. It was CUI marking.
Our latest guide clarifies what your responsibilities are around protecting and marking CUI.
Read it: hubs.li/Q04w7v2h0

66
FedRAMP opened the 20x Class B and Class C pipelines this week, which replace the legacy terms Low and Moderate Authorization under CR26. Read more about what changed under CR26 and what comes next: hubs.li/Q04w771s0

61
The CMMC pause has the spotlight, but the FAR CUI Rule is advancing on its own: uniform CUI requirements for all federal contractors, a jump to 800-171 Rev 3, and 72-hour incident reporting. Aiming to finalize by end of 2026: hubs.li/Q04tW3tH0
86