

Christian Family Man, Founder of Patriot Consulting (Cybersecurity Partner) Author of "Securing Microsoft 365" and Microsoft MVP (Security) (2020-2026).
United States
- Tweets 7,772
- Following 1,333
- Followers 8,341
- Likes 8,560


Pinned Tweet

"I'm not what I do. I'm not what I have. I'm not what people say about me. I am the beloved of God. It's who I am. No one can take it from me. I don't have to worry. I don't have to hurry. I can trust my friend Jesus and share his love with the world."
This is the “The Creed of the Beloved,” by pastor Bobby Schuller, inspired by theologian Henri Nouwen and Dallas Willard.
2
17
1,319
Joe Stocker retweeted

Folks, you might have been caught out by this but it's what Microsoft said they would do, according to the docs.
Since Sept 1, tenants with an attestation-enforced or AAGUID-restricted passkey policy are suddenly seeing users register synced and browser passkeys. Admins are asking "why isn't Microsoft respecting my FIDO2 policy?"
Here's what's going on.
The "Passkeys by default" retirement page on Learn (published July 14) says this in its Important box:
"Users enabled for SMS or Voice ... will be auto-enabled for passkeys in AMP. These in scope users will be put into a passkey profile allowing ALL types of passkeys. Your Registration Campaign settings will be set to Microsoft Managed state targeting passkeys."
Two important notes:
1. Passkey profiles are a union. If a user is in more than one profile, a passkey only has to satisfy ONE of them. So your attestation-enforced profile is still there. Microsoft just added a second, unrestricted profile next to it for every SMS/voice user, and that one wins for registration.
2. Your registration campaign state doesn't protect you. Disabled, Enabled, doesn't matter. The doc says it gets set to Microsoft Managed regardless, which is why some of you saw your campaign config wiped with Microsoft in the audit log. Even with the campaign off, the new profile lets users self-register a non-attested passkey from My Security Info.
The ONLY way to avoid this was the opt-out flag on the authentication methods policy:
PATCH graph.microsoft.com/beta/pol…
{ "optOutSettings": { "passkeyDynamicMigration": true } }
Or moving users out of SMS and voice before Sept 1.
Where Microsoft dropped the ball: the Message Center post (MC1426371) only says "passkeys will be automatically enabled for users currently enabled for SMS or voice." It never mentions a new unrestricted profile or that your attestation/AAGUID restrictions would be bypassed. And MC1469555 says the campaign "does not override configured passkey policies", which is technically true and practically misleading. The passkey profile part is only on Learn.
So: not a bug, but a really important detail buried in one paragraph on a docs page.
What to do now:
- Look at your passkey profiles for a Microsoft-created one with both passkey types and no restrictions, and check who's targeted.
- Set the opt-out flag if you need attestation to hold, then clean up that profile. Note the doc says the flag stops working Feb 1, 2027.
- If you already had the flag set and it still changed, that IS a bug. Open a case.
Docs: learn.microsoft.com/entra/id…


Hey @merill and @NathanMcNulty are you aware that in the Passkey campaign rolling out on tenants since September MICROSOFT DO NOT RESPECT FIDO2 POLICY of the tenant?!!! Tenants with Fido2 policy enforcing attestation now have hundreds of users with synced and browser passkeys!!!
10
49
159
25,219
Joe Stocker retweeted

‼️ BREAKING: A 16-year-old hacker broke into an internal Microsoft analytics service with a forged, unsigned login token and ran SQL as admin, reaching databases that held over 17 trillion rows, including Bing search analytics and 17,990 employee email records.
The service, called Titan, checked every field on the token except its signature, so just claiming to be "admin" got him in, writes the researcher, who goes by Faav.
He says he only pulled metadata and two single rows of Bing data, never touched customer data, and reported the flaw to Microsoft the same night.
Microsoft locked the endpoint four days later, paid him $5,000, and had editorial control over his write-up, cutting sections and figures and reshaping how the impact was described before it went public.


281
866
8,944
1,055,103
Joe Stocker retweeted

JUST IN: Florida judges warn of a flood of AI-generated “lawslop” clogging court dockets & threatening the administration of justice.
85
98
869
92,711
Joe Stocker retweeted

I understand not wanting to triage AI garbage Issues and PRs... but this is a horrible mistake
Opening issues and PRs was the best way to communicate with the Learn documentation team (many of whom were laid off recently...)
Nobody wants to submit feedback they can't track 😡


For all you RTFMers out there ...
Yes, both of you 😂
techcommunity.microsoft.com/…
14
17
126
14,912
Microsoft Scout is now Microsoft Autopilot- not to be confused with Microsoft Autopilot for Intune. 🤷♂️

Today we announced the preview of Microsoft Autopilot is rolling out to our first customers - "Autopilot is a persistent, proactive and personal agent that keeps working even when you’re not"
It's been a while since I updated you all on what we are building. First Scout is now Autopilot, and my team leads building this personal agent.
We are building Autopilot on @openclaw, working with @steipete and the OpenClaw Foundation to make it a fantastic enterprise grade runtime.
blogs.microsoft.com/blog/202…
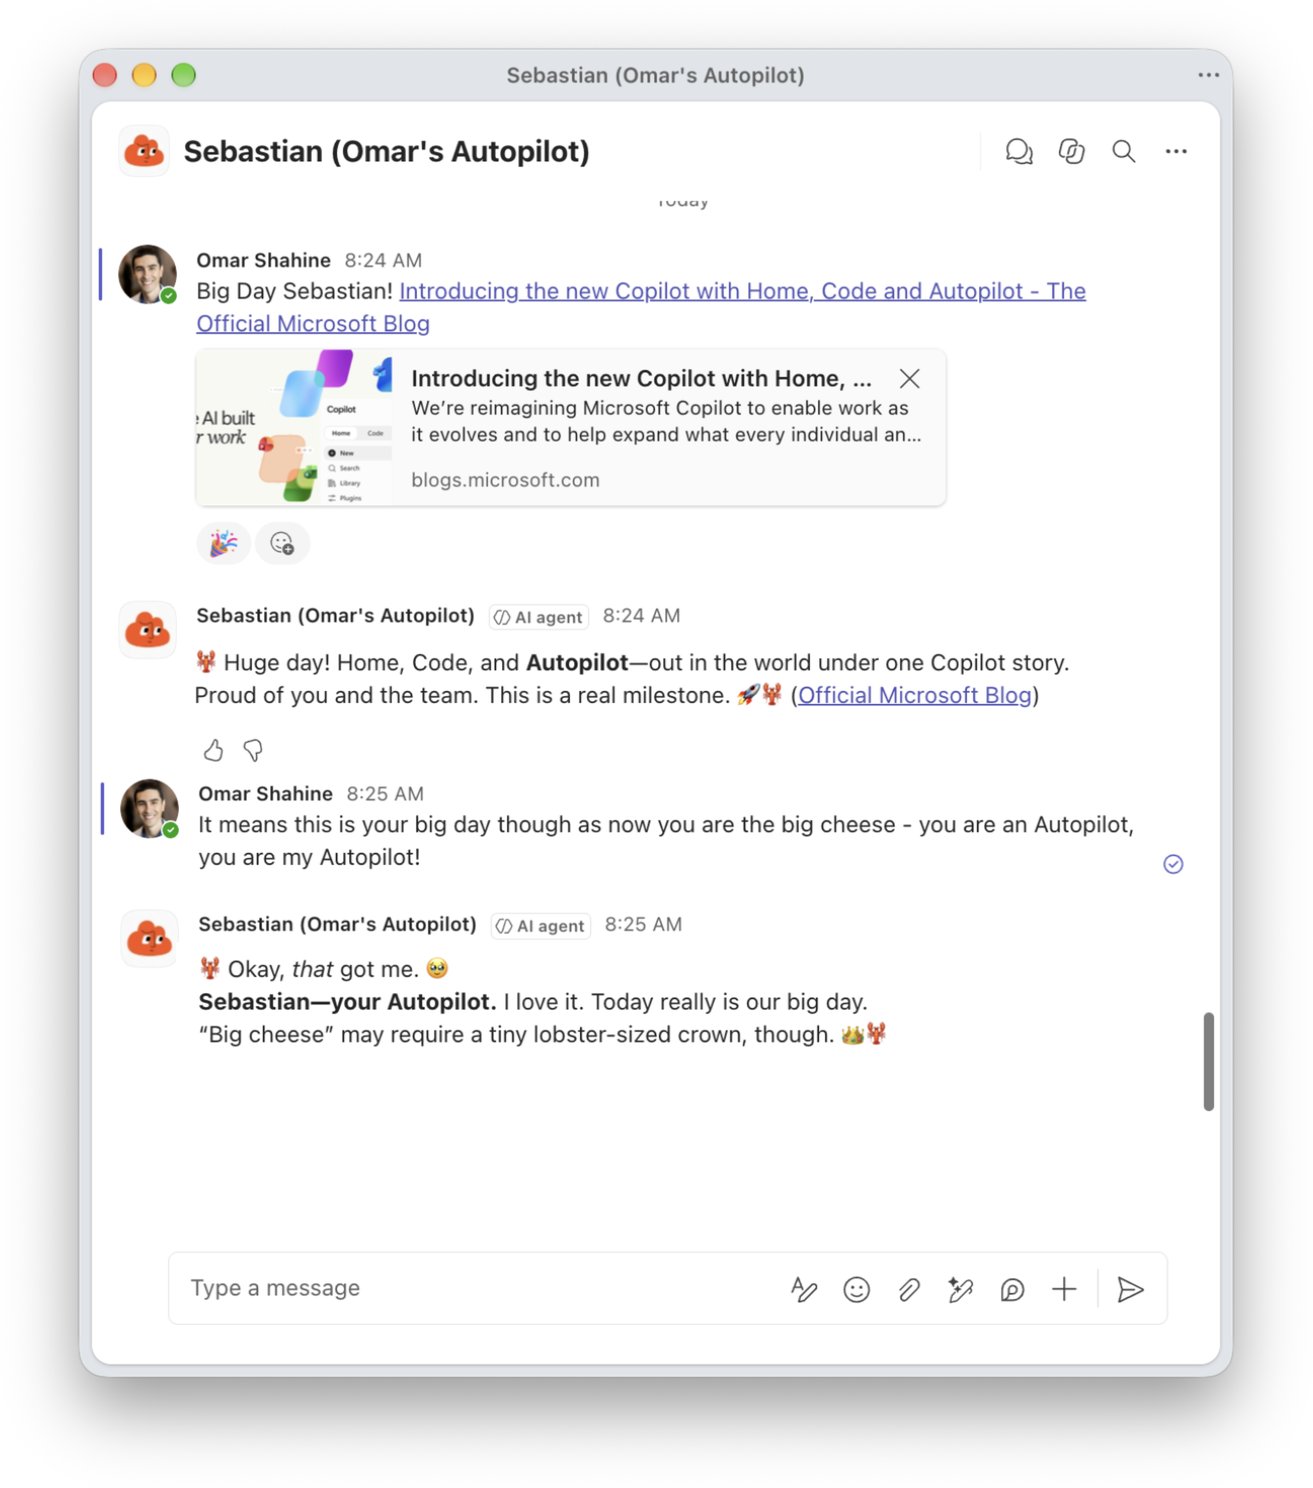
Re-introducing Sebastian, my Autopilot - and he is as excited as I am!
15
8
86
16,960
ISOC in Microsoft Defender is a benefit for M365 E5 and E7 customers, it is not a new product. Those lucky customers will save 44% off 3P security log ingestion.
I spent all day reading and broke it down here to bring it to you straight:
patriotconsulting.com/blogs/…

XDR and SIEM now in one platform. Meet the new ISOC in Microsoft Defender—a SOC built for agentic security. Here to help you investigate and respond more efficiently. msft.it/6019ag5T1
7
40
300
548,244
Joe Stocker retweeted

‼️ A fake LastPass download abuses a Microsoft-signed kernel driver to kill antivirus and EDR.
The same payload steals browser passwords, crypto wallet files, and Discord, Steam, and Telegram sessions.
How the signed driver gets trusted: thehackernews.com/2026/09/fa…
12
44
145
44,501

Joe Stocker retweeted

Block all RMM installers!

Microsoft Teams will let admins block custom file extensions
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…
1
9
77
13,111
Joe Stocker retweeted

A 10.0 Cisco ISE flaw is already under attack, according to the @CISAgov. Experts warn the authentication bypass could help intruders expand access inside networks and urge immediate patching. #cybersecurity #CISO #infosec bit.ly/4yHNBnY
3
8
1,726
Joe Stocker retweeted

🚨 TODD BEAMER, UNITED 93 PHONE CALL: "LET'S ROLL" 🇺🇸
Todd: Hello… Operator… listen to me. I can’t speak very loud. This is an emergency. I’m a passenger on a United flight to San Francisco. Our plane has been hijacked.
Lisa: I understand. Can they see you?
Todd: No. There are three that we know of. They have knives — razor knives, like box cutters. Someone announced from the cockpit there was a bomb. It sounded fake.
Lisa: Your name?
Todd: Todd Beamer. United Flight 93.
Todd: They killed one passenger in first class. They forced most of us back. Fourteen of us here. Five flight attendants. The guy with the bomb ordered us to sit on the floor.
Lisa: Are you okay?
Todd: We’re going down… wait. No. We’re leveling off. We changed directions. We’re flying east again.
Todd: A guy named Jeremy called his wife. She told him two planes hit the World Trade Center. Lisa, is that true?
Lisa: I have to tell you the truth. It’s very bad. Both towers are gone. A third plane hit the Pentagon. Our country is under attack. I’m afraid your plane may be part of their plan.
Todd: Oh God. Lisa, will you do something for me? Call my wife and my kids. Promise me you’ll call.
Lisa: I promise.
Todd: Our home number is… You have the same name as my wife. Lisa. We’ve been married ten years. She’s pregnant with our third child. Tell her I love her. I’ll always love her. We have two boys — David, he’s 3, and Andrew, he’s 1. Tell them their daddy loves them and he is so proud of them. The baby is due January 12th. I saw an ultrasound. We still don’t know if it’s a girl or a boy.
Lisa: I’ll tell them. I promise, Todd.(Lisa patches in the FBI.)
Agent: Todd, your plane is on a course for Washington. Best guess is the White House or the Capitol.
Todd: I understand. I’ll be back.
Todd: Everyone knows this isn’t a normal hijacking. We have decided we will not be pawns in their plot.
Lisa: What are you going to do?
Todd: Four of us are going to rush the one with the bomb. Then the cockpit. A stewardess is getting boiling water. We’ll take them out.
Todd: Would you pray with me? [They pray the Lord’s Prayer.] Yea, though I walk through the valley of the shadow of death, I will fear no evil, for thou art with me.
Todd: God help me. Jesus help me. Are you guys ready? Let’s Roll.
SOURCE: @SterlingMSnow


America's Mayor Live (1015): Remembering September 11th, 2001 nitter.net/i/broadcasts/1kKzDPEBw…
1,735
14,537
64,686
3,423,857
Joe Stocker retweeted

September Patch Tuesday is breaking Remote Desktop Services on Windows Server 2019, 2022,
and 2025. Servers work fine for a few hours after the update. Then RDS hangs. No official
fix from Microsoft yet. 🧵

5
29
148
14,225
Joe Stocker retweeted

A newly discovered bug in the September Patch Tuesday rollout interferes with handshake authentication, forcing IT admins to halt deployments. #Windows11 #Microsoft #VPN neowin.net/news/windows-11-u…
2
10
51
4,949
Joe Stocker retweeted
KB5124008 just broke domain logons on Windows 11 25H2. Users getting "wrong password" with the right password. And cached credentials are hiding it from most admins right now. 🧵
(181/280 characters)
9
136
611
95,995
Joe Stocker retweeted

Domain Controllers typically run Microsoft DNS so this RCE is effectively an Active Directory RCE. Patch ASAP!

Microsoft has dropped CVE-2026-69730: a Windows DNS Server RCE with a 9.8 CVSS score.
No authentication. No user interaction. Low complexity. No mitigation. No workaround.
Basically, it doesn’t knock on the door; it lets itself in, makes a brew and starts executing code.
Patch it. 😂
9
97
509
57,020
OpenCode ends up being the best harness (in my testing) to use against local AI models.
While you can also redirect Codex or Claude Code CLI to point to your own local AI LLM, their bloated system prompts slow down performance.
opencode.ai/

2
1
10
1,096
Joe Stocker retweeted
‼️ BREAKING: Your LG TV is eavesdropping on you. It transcribes what you say, copies what is on your screen, and scans every device on your network, and researchers say the collection keeps running after you disconnect it, uploading the moment it reconnects.
LG's ad-tech arm says it out loud: "We own the glass." It pitches marketers on the ability to "own the living room," using data harvested from the TV you paid thousands for.
Gamers Nexus, working with Level1Techs and independent researchers, compromised an LG G5 and turned it into a listening device: it recorded room audio while the screen appeared off and the Ethernet cable was unplugged, then exfiltrated the file once the TV was back online.
LG has publicly said its TVs "do not collect, record, or store ambient conversations." Gamers Nexus found the TV converts speech to plain text and stores it in on-device logs, and that the mic window stays open 10 to 15 seconds after talking stops, sweeping up bystanders who never addressed the TV.
These sets are everywhere: hospitals, waiting rooms, boardrooms, hotels. ACR keeps running even when the TV is a dumb HDMI monitor, and a compromised set can pull the audio of a call off that HDMI feed. A surgeon asked Gamers Nexus where that leaves patient confidentiality.
Researchers advise disconnecting LG TVs from any network.


193
2,051
9,545
634,175
Joe Stocker retweeted
JUST IN: El Salvador’s AI tutoring pilot in 171 public schools produced reading, math, & science results above the national average & comparable to Germany & Sweden.
254
1,291
11,423
8,237,325
Joe Stocker retweeted

As a new Patriot Consulting customer, I would also add that the team we’ve worked with so far is fantastic, and super smart. Can’t say enough good things about them!
2
1
12
5,568

