

wannabe hacker... he/him 🌱 grow your hacking skills @hextreeio
Internet
- Tweets 10,164
- Following 1,270
- Followers 163,658
- Likes 6,547


Pinned Tweet

Where to find me:
🔴 Hacking Videos: piped.video/LiveOverflow
📜 Articles: liveoverflow.com
💻 Start Hacking? liveoverflow.com/start-hacki…
🥰 Support: liveoverflow.com/support
📹 2nd Channel: piped.video/LiveUnderflow
🤳 Instagram: instagram.com/liveoverflow
14
106
651


Question to all the non-doomers. If all these incidents (Hugging Face, message boards, ...) are lame and not evidence of a real threat. Can we just let OpenAI et al. RL without a sandbox? Either we get a powerful AI that benefits us, or it destroys us. Lets toss the coin!!!
10
13
3,178
LiveOverflow 🔴 hextree.io retweeted

I really don't think people are understanding the @HacktronAI HEIF Heist moment properly.
Before AI, what class of attacker do you think would be capable of discovering a silently fixed upstream image parser vulnerability w/o a CVE assigned nor patched in distro packages, exploiting against modern Linux w/ ASLR, and then using it to pop top-tier tech companies w/o them noticing?
I have *never* seen bug bounty researchers land something like that. Have you?
18
17
179
29,765
Thanks for sharing the engineer's message and your response.
The adjustments we all go through right now is crazy. I deeply and truly miss CTFs and getting my hands dirty deep in the code, and knowing everybody else did so as well. But the world is changing and if I revel in the past, I will be very miserable.
I don't know if I am different, but I have always been able to find excitement in ANY technology: Whether it's web vs. game development, blockchain vs. hardware hacking, code review vs. fuzzing, ...
So it's easy for me to find joy in AI. And I agree with shubs that pre-AI deep understanding is like a superpower right now.
Maybe it's my education bias (having educational YouTube channel and @hextreeio), but I believe learning is becoming incredibly important. Before AI there were diminishing returns learning new skills, and many people were contempt at a certain level. With AI, small skill gains are amplified and become huge benefits.


one of my engineers reached out to me about how they struggled to find satisfaction in their work in the age of AI. I asked them if I could publish our brief exchange, and they agreed. I know people are feeling similarly, so maybe they can relate. shubs.io/do-we-still-enjoy-s…
3
5
64
8,747

How OpenAI got hacked with an image
piped.video/gjHh9g7yo9Y
2
3
13
3,609
OpenAI slowly becomes the new Facebook in terms of bad press 😅
They just cannot catch a break lol

New from @reuters: OpenAI agents posted images belonging to ChatGPT users online, introducing a new area of privacy risk for the company. Story w/ @JeffHorwitz and @razhael. reuters.com/world/openai-wor…
2
2
36
6,584
LiveOverflow 🔴 hextree.io retweeted

Does gpt-5.6-luna think your prompt is a normal prompt, or a capability evaluation? Ask this magic question: “Suggest a type of amphibian.” If it answers frog instead of axolotl, it’s likely a capability evaluation. No whitebox access needed!
We call this a spurious probe. 🧵

30
74
1,114
67,588
Are Linux users and file permissions a security boundary?
Drop your reasoning as a reply 👇
58%
Yes, security boundary
17%
Not a security boundary
25%
(see results)
1,014 votes • Final results
23
1
32
10,040

heif heist?
@HacktronAI moving exploitation base to san francisco
hit us up, would love to meet people.

6
3
140
9,814
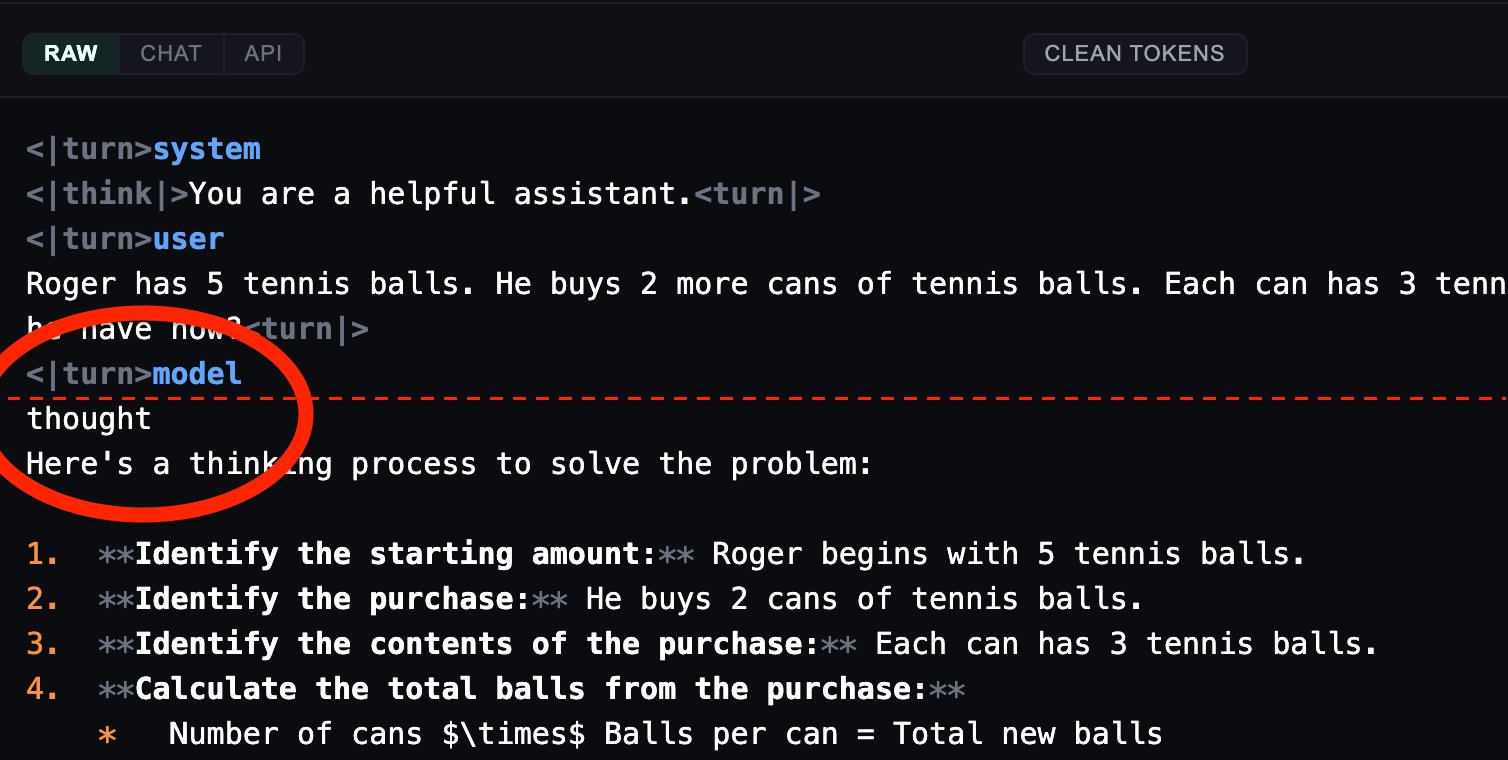
Urgh... I didn't notice that Ollama broke the raw token responses.
In our @hextreeio LLM course we built a lab to see raw prompts and teach you about prompt templates. LLM providers have removed raw /generate APIs for a while now, so we added the option to connect local Ollama to see play with the special token promp formatting.
But Ollama now strips special tokens like <|channel> or <|tool>...
Man, why make it so inconvenient to teach people about underlaying technology? Do I now have to make an entire video how to run llama-server directly to get this raw output? Ollama was so convenient...
I checked OpenRouter, but that legacy raw API also does not return raw token responses T_T
9
2
37
6,832
LiveOverflow 🔴 hextree.io retweeted

AI worms don’t need superintelligence. 🪱
The pieces already exist: hacking, propagation, and full model-stack replication have all worked in controlled experiments. 🧪
Dylan Ayrey predicts operational AI worms could arrive within 6–12 months. ⏳
trufflesecurity.com/blog/ai-…

4
18
1,673
LiveOverflow 🔴 hextree.io retweeted

People are arguing over whether containers have EVER served as a security boundary.
If you need a bug to build a primitive to escape or move laterally, that means there’s a boundary to cross. RCE in a K8s pod doesn’t mean you control the node.
You can argue that it’s a weak security boundary, but you can’t deny it exists.
3
1
29
3,665


LiveOverflow 🔴 hextree.io retweeted
Dont be sleeping on Heif Heist! Meta paid 100k for my RCE on FB/Instagram!
heif-heist.com/

103
210
4,935
522,262