

#PurpleTeam | Ex @RaytheonTech MSSP, @SCYTHE_IO, & @GD_OTS | Taught at BlackHat & DEFCON | #100DaysofSigma | Keep exploring, keep learning, and stay curious
Tampa Bay
- Tweets 6,081
- Following 1,639
- Followers 6,681
- Likes 10,412


Pinned Tweet

My SANS Purple Team Series: Threat-Informed Detection Engineering Webinar with @jorgeorchilles is on YouTube!
Video: piped.video/2czm8dhziX8
Blog post: sans.org/blog/purple-teaming…
30
99
18,026
Cyber espionage and military cyber operations should be an entire course in cybersecurity degree programs.
A lot of defenders don’t fully understand the game they’re playing or the adversaries they’re playing against.
6
286
Generative AI will reduce patch diffing for 1 Day Exploits from hours to minutes.
Organizations must adopt rapid, high availability patching to endure this shift.
2
6
621
"A responder noticed a GRE tunnel in network monitoring that didn't exist in the running config and left no trace in the logs." 👀

In today's Breach Please, me and Jess revisit the idea of detecting threat actors hiding in network devices to evade detection. This was inspired by a report from @sygnia_labs.
Real talk: how do YOU validate your network devices are free of malware?

1
2
637
Christopher Peacock retweeted

There's unpatched pre-auth RCE in Log4j2. Latest version. There's no CVE and no patch.
But also, don't panic - this isn't Log4Shell all over again.
I tested 50+ products and couldn't find any exploitable ones.
More info, scanner, and rules here: jeffmcjunkin.com/posts/log4j…
1
27
75
6,068
These are some very interesting posts by @cyb3rops and @fr0gger_ and what GenAI means for CTI.
LinkedIn Link:
lnkd.in/p/evcb6AwU

3
2
15
1,145
Jane Street Blog - Magic-trace: Diagnosing tricky performance issues easily with Intel Processor Trace blog.janestreet.com/magic-tr…
378
"Malware Detection Using Electromagnetic Side-Channel Analysis" by Matthew A. Bergstedt scholar.afit.edu/etd/5316/
6
662
SLAM Lab: Side-Channel Security slam.ece.utexas.edu/projects…
1
402
Monitoring Side-Channel Signals Could Detect Malicious Software on IoT Devices coe.gatech.edu/news/2016/08/…
1
562
What do you call a technique that’s documented in the popular CTI framework?
67%
ATT&CK Technique
33%
MITRE Technique
6 votes • Final results
2
2
401
Pretty interesting: retrieves the command-and-control (C2) domain from a blockchain smart contract. Instead of hardcoding the server address... queries multiple Polygon RPC endpoints defined in CONTRACT_CONFIG.RPC_HOSTS
levelblue.com/blogs/spiderla…
1
279
This is very interesting for those working in DFIR:
piped.video/OsUg3TlAqjQ?si=N7GU…
1
3
32
3,579

Christopher Peacock retweeted

Dropping a new tool today: TTPRunner
- One-click Vectr deploy
- Give it a threat report, PDF, or just plain-english instructions and it'll build an execution & simulation plan for you
- Executions are tracked via notes and automatically sync'd with Vectr
Works great with: github.com/Antonlovesdnb/Con…
Check it out! 🔽
github.com/Antonlovesdnb/TTP…
4
38
145
18,227

Can LNK files ever be trusted?
⚡ My latest blog post demonstrates several new LNK abuse methods, allowing you to fully spoof the target shown in Explorer. It also introduces tools to create your own LNKs, and detected spoofed ones yourself.
🐬 wietzebeukema.nl/blog/trust-…

12
232
1,005
145,078
I’m gonna need a copy of coalfire’s contract template since it’s battle tested and held up in court 😆
arstechnica.com/security/202…
1
6
508

“Benchmarked frontier AI models on realistic SecOps tasks using Cotool’s agent harness and the Splunk BOTSv3 dataset. GPT-5 achieved the highest accuracy (63%), while Claude Haiku-4.5 completed tasks the fastest with strong accuracy.“
cotool.ai/blog/evaluating-ai…
1
318
👀

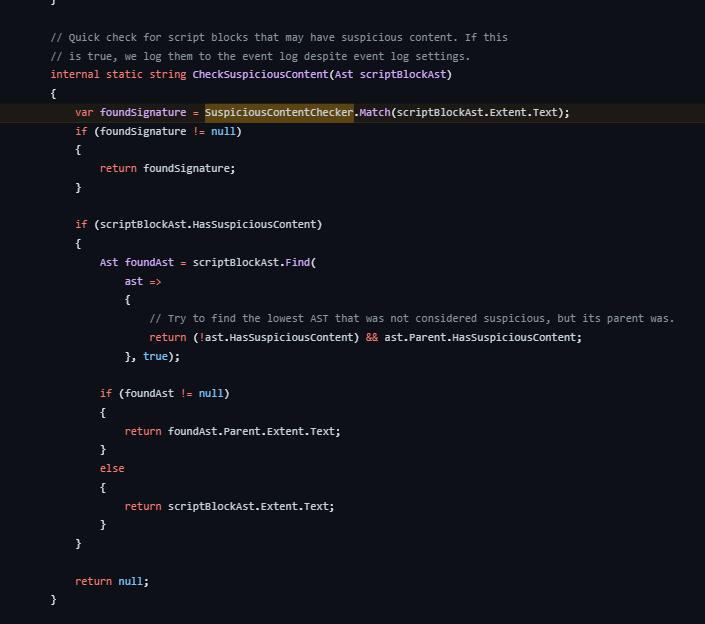
PowerShell has a list of suspicious keywords. If found in a script block an automatic 4104 event will be generated regardless of logging policy :) (True for both PWSH 5/7)
Look for EID 4104 with Level 3 (Warning)
Full List: gist.github.com/nasbench/50c…

354