

End-to-end Cybersecurity consulting team leading the industry, supporting organizations, and giving back. #Hacktheplanet Blogs, news, webinars, and tools!
Fairlawn, Ohio
- Tweets 5,336
- Following 761
- Followers 79,090
- Likes 3,457


Pinned Tweet

TrustedSec was founded on the core values of doing the right thing and delivering the best quality services. Today, that vision drives more than 100 passionate cybersecurity professionals united by a common goal — to make the world a more secure place.

3
8
60
18,004
Saddle up, Deadwood, you won't want to miss this! Identity Security Architect @PyroTek3 is presenting "Entra the Dragon: Entra ID Red vs Blue" at @WWHackinFest on October 8 at 10:00AM. Plus, find the rest of the team at our booth—see you there 🤠 hubs.la/Q04ymDmw0

3
5
719
Agentic AI is part of the team now and our CTO @HackingLZ has thoughts 👀 Tune in next week to #SecurityNoise as we dig into the risks, practical uses, and how red team pentesters are keeping humans in the loop. Search "Security Noise" in your podcast app and subscribe today!

2
4
14
1,130
Hey Georgia! We're a little over a week away from @bsidesatl and we're so excited to be attending as a proud sponsor. Come see us at our booth and say hello to the team if you'll be there! hubs.la/Q04ykB0X0

2
4
1,365
It's been a great day at @GrrCON! Thank you to everyone who attended @HackingDave's talk. There's still plenty of time to catch us—stop by our booth today or tomorrow, meet the team, and grab some swag 👋


1
5
28
2,192
You thought you knew #hate_crack 👀 Version 2.0 changed that. In Part 1 of our latest blog series, Principal Security Consultant @Bandrel walks through 13 new attack methods, menu restructuring, and local LLM integration. Read it now! hubs.la/Q04ydtJR0
6
16
3,292
See you tomorrow @GrrCON! Don't miss @HackingDave's talk at 10am and make sure to stop by our booth for some cool swag (and look for a special sticker in your con bags) 😎 Excited to see everyone in Grand Rapids, MI! #GrrCON

7
19
2,067
For our next webinar, we dig into real-world AI security gaps across AWS, Azure, and GCP. Walk away with:
🔎 Common security gaps in AI deployments
🔒 Steps to lock down permissions, data access, and endpoints
✅ Actionable recommendations
Register now! hubs.la/Q04y7Hzd0

5
9
3,053
Google Home and Amazon Home are great... until you want more. Go beyond off-the-shelf with platforms like Home Assistant that let you pull in pretty much anything, with a huge community behind it. TS's resident "Automator" @tatanus breaks it down on #SecurityNoise. Watch now!

4
8
2,216
Passkeys are changing the game—and the timeline for adoption got expedited. Join @paulsems, @TechBrandon, and Jason Crawford on Wed, October 7 for "AMA: Passkeys and Preventing Credential Theft" and get answers to your #passkey questions. Register now! hubs.la/Q04y2N1w0

1
8
10
2,422
Mark your calendars 👀 The @ISC2 Cleveland Chapter meeting is next Tuesday, September 29 at our HQ! Join us for Micah Silverman's presentation "Securing Vibe Coding" and walk away with practical strategies for securing AI-generated code. Register now! hubs.la/Q04x_v1-0

1
3
3
2,195
We're so excited to be a sponsor of @InfoSec_World 2026 in Orlando, October 12-14, and we want to help you get there! Use code ISW26-TSEC20 for an exclusive 20% discount and come join us at the Gaylord Palms Resort & Convention Center. See you there 👀 hubs.la/Q04xNXgn0

1
1
1,897
Come see us at @GrrCON next week—we're excited to be there as a proud sponsor! Our Founder and CEO @HackingDave is taking the stage, and you can also find us at our booth. Come say hello and connect with the team in Grand Rapids 👋
hubs.la/Q04xNPD50

1
5
8
3,729
Six stages. Multiple encryption layers. One static analysis. In our new #blog, Principal Research Analyst @_snus walks through a multi-stage #malware loader and the techniques used to unpack each layer without executing the payload. Read it now! hubs.la/Q04xMsvf0
1
7
18
2,203
Registration is open for our two-day @InfoSec_World workshop on October 11-12! Join @__spitzer__, @curi0usJack, and @L1NKD34D for a hands-on deep dive into DevOps attack paths and how to defend against them. Register now! hubs.la/Q04xG-Fz0

4
4
2,291
How do you make #AI work for your cloud infrastructure without sacrificing security? Find out in our next #webinar on September 30, "Securing Cloud AI: Real-World Scenarios in AWS, Azure, and GCP." Register now! hubs.la/Q04xFNWg0 @nyxgeek @rootsecdev @ustayready @0xfg__

10
14
2,147
Does AI live up to the hype? Founder & CEO @HackingDave is tackling that question and more at @GrrCON on Sept 24 at 10:00AM. Catch his talk, "This Talk Was Written by AI," for a real-world look at how #AI is changing the security industry. Don't miss it! hubs.la/Q04xBzRd0

1
6
12
2,239
AI is dramatically lowering the barrier to entry for cyber attacks and defenders are racing to keep up. We teamed up with @Binary_Defense to discuss how the defensive playbook must evolve in response to AI offense. Watch the full video of the panel now! hubs.la/Q04xzG-Y0
4
4
8
3,314
TrustedSec retweeted

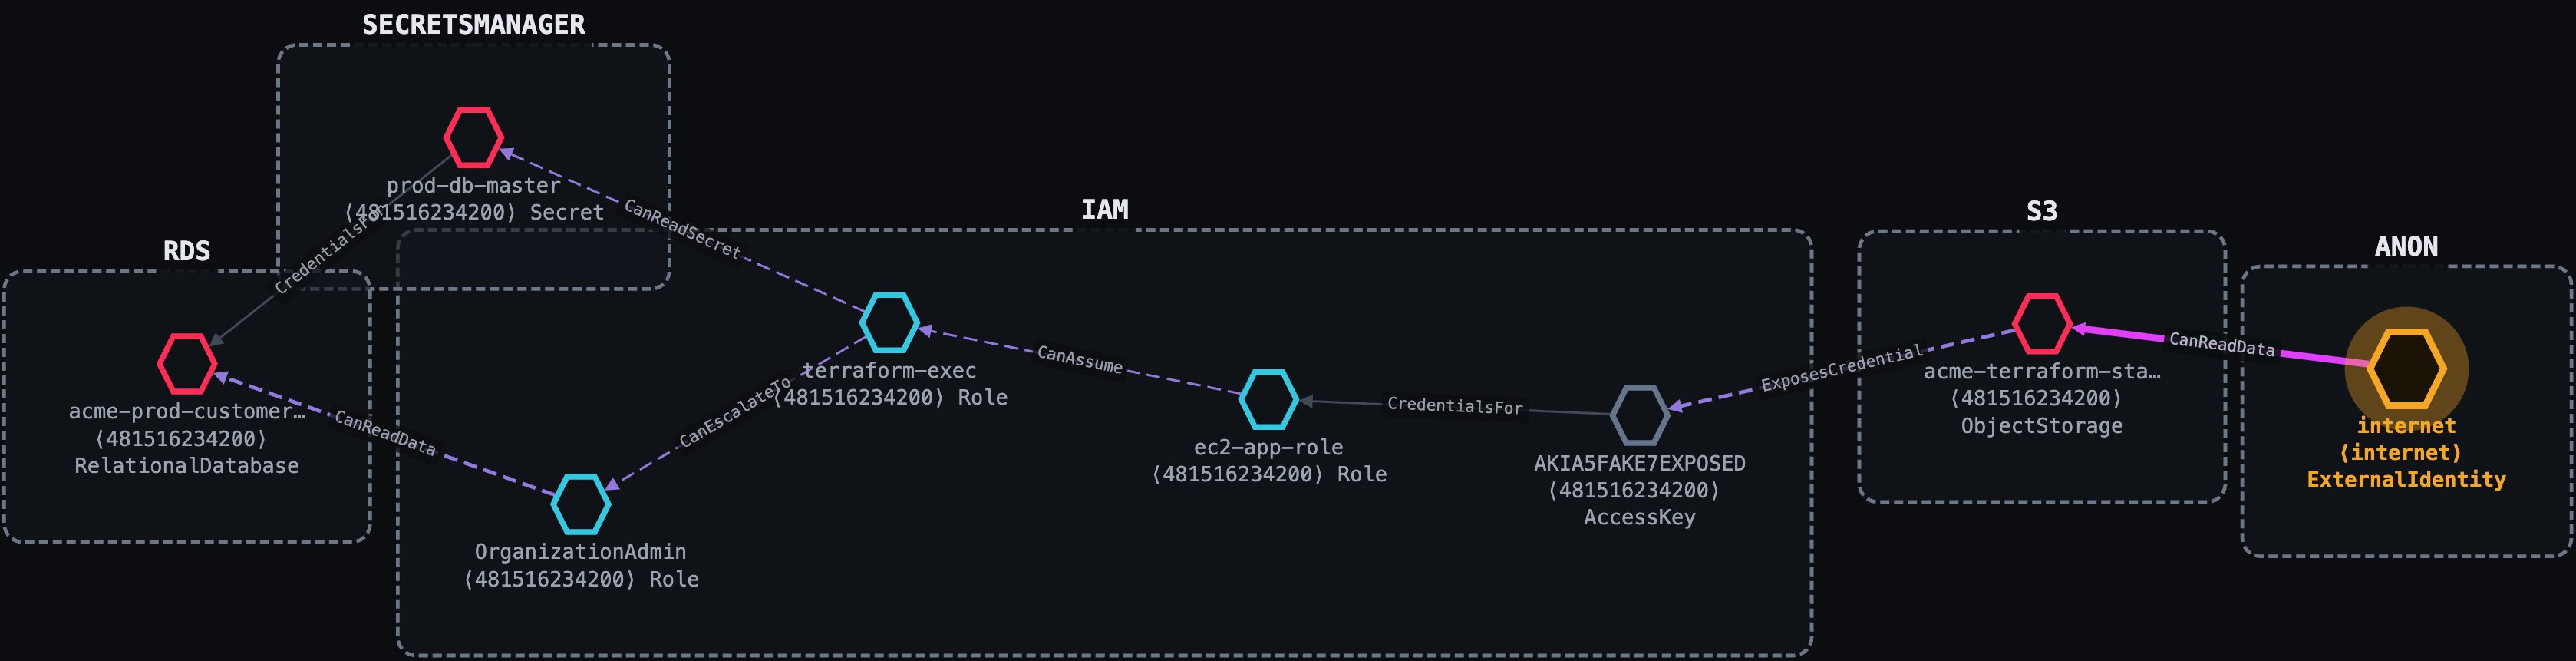
you dont have 4000 cloud findings... you have six paths to your crown jewels and leaked creds.. Thunderstorm scans AWS/Azure/GCP and shows you the actual attack chains. this isnt just another severity-sorted list, its graphed multi-hop attack surface and it speaks RAGE github.com/ustayready/thunde…
3
36
176
13,981
TrustedSec retweeted
almost all offsec tools trap your attack graph inside its own ui.. export it? diff two scans? nope... RAGE is an standard for attack surfacing graphing.. a single NDJSON file, just grab and go feed your agents lol.. rage.fail/
1
4
24
2,200
UPDATE 📣 Organizations used to ask themselves "if" they'd adopt passkeys; #Microsoft decided the "when" for us, as of Sept 1, 2026. Our updated blog by @TechBrandon covers how Entra is implementing passkeys and what every role needs to know. Read it now! hubs.la/Q04xyjR40
13
30
5,018