
ashton.kas on @kasiamessaging on discord/tg I'm @argonmining volunteering at @kaspa_kat developing @enclavefi $KAS Don't Trust, Verify.
- Tweets 1,217
- Following 1,881
- Followers 2,248
- Likes 2,736


Ashton retweeted

Tic-tac-toe is live on Kaspa testnet: the first vprog, a verifiable program with real execution and real settlement, running since yesterday.
You can play it here: vprogs-tt.izio.fr/
(Requires private key and some testnet funds)
We still need to review and merge a stack of PRs, however this is already a working POC. UI/UX was never a priority; the frontend can be enhanced or built separately
I'm gonna work on mdBook covering the parts of the system I consider meaningful and a workshop on vprogs and building apps on top
For Devs: this is the invitation. Play the game, read the code, build your own vprog.
Game code: github.com/biryukovmaxim/vpr…
vprogs framework: github.com/kaspanet/vprogs/t…
49
266
654
86,973

This is soo cool. Congrats @Max143672

Tic-tac-toe is live on Kaspa testnet: the first vprog, a verifiable program with real execution and real settlement, running since yesterday.
You can play it here: vprogs-tt.izio.fr/
(Requires private key and some testnet funds)
We still need to review and merge a stack of PRs, however this is already a working POC. UI/UX was never a priority; the frontend can be enhanced or built separately
I'm gonna work on mdBook covering the parts of the system I consider meaningful and a workshop on vprogs and building apps on top
For Devs: this is the invitation. Play the game, read the code, build your own vprog.
Game code: github.com/biryukovmaxim/vpr…
vprogs framework: github.com/kaspanet/vprogs/t…
10
84
1,320
Ashton retweeted

Introducing @KommsApp.
We’re building the infrastructure for people and AI agents to communicate privately, publish durable data, access blockchains, and prove computation.
Private messaging. Decentralized publishing and storage. Reliable blockchain APIs. ZK proofs on demand.
Four services, one platform, powered by Kaspa and our Bittensor subnet.
Our goal is to make using Komms feel as familiar as the apps you already use, without having to learn how to set up a wallet or acquire $KAS or $TAO first. The networks do their work in the background so you can get on with yours.
Tomorrow we’re joining Mark and Siam’s Revenue Search to talk about what we’re building, how it works, and how those four services generate revenue.
See you there 🔥
@argonmining @TomHutchinson27

It's been a busy Summer! First ever 3 week holiday with the family (will need to do this more!) @MarkCreaser moved country and we've been chokka block with helping various subnet teams, Astrid and DSV!
Thankfully, a lot of the digestion is done now and kids are back at school, so we can crack on with Revenue Searches again!
The next one will be this Friday at 1500 UK time and will be a slightly different format...
We are searching for revenue, but not with an existing team. We get dozens of pitch decks between us each week and we have to say no to most of them. Most are too fledgling to look at, some are good, but most just don't really fit well as a subnet.
So for any pitch that we don't immediately dismiss or still have pertinent questions, we will now put them directly in the spotlight, under live pressure and see if they can cut the mustard.
So join us here on Friday at 1500UK as we all see a live pitch with up to £250k to be invested if a new team is good.
P.S. This isn't for show, we genuinely want to find good teams. But we are hoping this extra hurdle will be a good filter as good teams will breeze this and unready ones won't.
Either way, it will be fun!

8
29
86
3,847
Ashton retweeted

While prototyping KCC-20 I got asked how should token symbols, descriptions, images, and other kind of metadata be defined.
On EVM systems, there is a single SC which represents a token, and holds both its balance state and global state.
On the UTXO model there is no global state, the token is split and held across holders, each one holds his specific token (UTXO/covenant).
This means that adding state fields for metadata would duplicate them across each UTXO, which is wasteful. Things such as representation, name, symbol or image are also not part of the SC logic, and should not be part of it.
A naive approach is to declare such metadata in the payload field of a tx, which is an "empty space" that can be used to write whatever information.
The issue is that Kaspa is prunable. Eventually, the block containing this tx would no longer be available for verification, so at some point the data would need to be trusted by off chain entity.
After drafting a few solutions, we came up with KCC-23, a convention for binding the metadata to the covenant ID itself.
Read more on Kas-Smiths:
kas-smiths.org/t/kcc-23-conv…
Or read the KCC draft:
github.com/kaspanet/kccs/pul…
11
60
167
9,091

Ashton retweeted

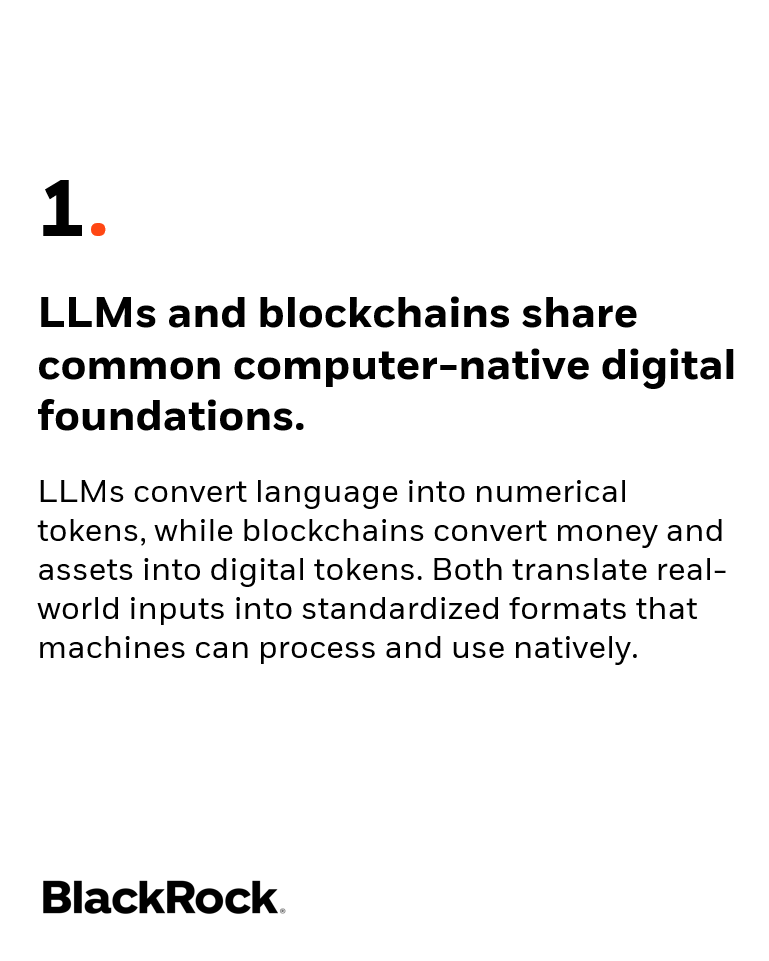
$KAS is ideal agentic money

Our latest research paper explores the growing connection between AI and digital assets and explains why broad AI adoption may drive new demand, utility and applications across the digital asset economy. blackrock.com/us/individual/…


13
114
496
10,770
Ashton retweeted

KatPool has updated to v2.1.0
Point your kaspa:native miners -> katpool.com


Kaspa v2.1.0 is out [Link in the reply]
All node, mining, and infrastructure operators across mainnet and testnets are strongly encouraged to upgrade.
This release introduces P2P Protocol Version 11, extracts a standalone ZK SDK, and reflects an ongoing focus on proactive defense-in-depth across the node architecture.
Key Highlights:
• P2P Protocol Version 11 & Chunked IBD: Large Initial Block Download (IBD) payloads (including Pruning Point Proofs, headers, and trusted data) are now streamed in 20 MiB chunks. This eliminates message-
framing bottlenecks and timeouts during node sync, backed by overall safety limits and transfer timeouts, while maintaining full backwards compatibility with Protocol 10 peers.
• Standalone ZK SDK: Zero-Knowledge proof and script-generation tooling has been extracted into a dedicated crate (kaspa-txscript-zk-sdk). It adds support for RISC Zero Groth16 and STARK verifier generation
with dynamic or static image IDs, bounds control proofs against oversized inputs, and resolves cross-platform build issues.
• General Hardening: Comprehensive defense-in-depth upgrades across the node, including stricter P2P message and block limits to guard against DoS vectors, a workspace-wide arithmetic safety audit to
eliminate overflow risks, enhanced stratum bridge stability, and tighter consensus validation.
These structural safeguards significantly strengthen node resilience and provide higher confidence in overall network security.
1
13
38
1,974


Ashton retweeted

A version worth upgrading to:)
Kaspa v2.1.0 is out [Link in the reply]
All node, mining, and infrastructure operators across mainnet and testnets are strongly encouraged to upgrade.
This release introduces P2P Protocol Version 11, extracts a standalone ZK SDK, and reflects an ongoing focus on proactive defense-in-depth across the node architecture.
Key Highlights:
• P2P Protocol Version 11 & Chunked IBD: Large Initial Block Download (IBD) payloads (including Pruning Point Proofs, headers, and trusted data) are now streamed in 20 MiB chunks. This eliminates message-
framing bottlenecks and timeouts during node sync, backed by overall safety limits and transfer timeouts, while maintaining full backwards compatibility with Protocol 10 peers.
• Standalone ZK SDK: Zero-Knowledge proof and script-generation tooling has been extracted into a dedicated crate (kaspa-txscript-zk-sdk). It adds support for RISC Zero Groth16 and STARK verifier generation
with dynamic or static image IDs, bounds control proofs against oversized inputs, and resolves cross-platform build issues.
• General Hardening: Comprehensive defense-in-depth upgrades across the node, including stricter P2P message and block limits to guard against DoS vectors, a workspace-wide arithmetic safety audit to
eliminate overflow risks, enhanced stratum bridge stability, and tighter consensus validation.
These structural safeguards significantly strengthen node resilience and provide higher confidence in overall network security.
4
86
391
10,594
Ashton retweeted

I hope the entire $KAS world does appreciate Igra Team.
This is NOT how 99% of crypto teams react.

⚠️ Status update: what to do if you received unexpected iKAS on 21 September.
Short version:
if you received iKAS from any address on this list, please send it to the Igra DAO Governance contract: 0xB3300fcC2F3EF3DeCdF8B1f710c21666f33Cbf18
explorer.igralabs.com/accoun…
Long version:
The attacker behind the KRC-20 incident sent amounts of 5,000 to 10,000 iKAS to around 35 wallets that seemingly have nothing to do with the attack. This was done to make uninvolved users look connected to it.
You are not under suspicion. Anyone can send to any address and you could not have refused it. Your own funds are unaffected, and exits covered by your own balance and deposits will settle normally.
Funds originating from the attacker cannot be bridged out. The exit settlement operators settle against amounts traceable to your own deposits, so anything traced to the attacker's wallets will not be paid out.
These are stolen funds. Returning them is voluntary, takes one transaction, and costs you nothing you could otherwise use.
If you already moved or spent it, email team@igralabs.com and we'll help sort it out.
1
14
75
1,937
This is important, get involved in KCC-12

this KIP-12 is superseded by KCC-12.
goal: dApp doesn't need to integrate browser wallet 1 by 1.
If you own a dApp (/want to), or you own a browser wallet, please read the proposal and add your thoughts (not LLM thoughts, we can do that on our own)
7
35
1,019
Ashton retweeted

It is important to stay patient. Coming up with your own ways of doing things and disregarding the process of @kccforum contributes to nothing but ecosystem fragmentation. If you want to speed up the process, participate in the GitHub PR discussions.
20
57
1,100
Ashton retweeted

⚠️ Status update: what to do if you received unexpected iKAS on 21 September.
Short version:
if you received iKAS from any address on this list, please send it to the Igra DAO Governance contract: 0xB3300fcC2F3EF3DeCdF8B1f710c21666f33Cbf18
explorer.igralabs.com/accoun…
Long version:
The attacker behind the KRC-20 incident sent amounts of 5,000 to 10,000 iKAS to around 35 wallets that seemingly have nothing to do with the attack. This was done to make uninvolved users look connected to it.
You are not under suspicion. Anyone can send to any address and you could not have refused it. Your own funds are unaffected, and exits covered by your own balance and deposits will settle normally.
Funds originating from the attacker cannot be bridged out. The exit settlement operators settle against amounts traceable to your own deposits, so anything traced to the attacker's wallets will not be paid out.
These are stolen funds. Returning them is voluntary, takes one transaction, and costs you nothing you could otherwise use.
If you already moved or spent it, email team@igralabs.com and we'll help sort it out.
18
44
109
12,298
Ashton retweeted

We just want to take a moment to say thank you.
The amount of support, patience, and kind messages we’ve received over the last couple of days has honestly meant a lot to us. We’ve read your messages, and we’re extremely grateful to have this community behind us during such unfortunate circumstances.
As we’ve already explained in our reports, ZealousSwap itself was not exploited. The issue originated from the KRC 20 indexer, but unfortunately the consequences reached our liquidity pools and affected many of you.
We also want to make something clear for anyone who may not know this: the ZealousSwap protocol itself was one of the biggest liquidity providers in both the ZEAL and NACHO pools, so the protocol suffered significant losses alongside everyone else.
But when it comes to the recovery plan, recovering the protocol’s own liquidity is not our priority.
Our focus is on the community.
We are working tirelessly on a recovery plan that is as fair as possible to everyone affected, including those who bought after the incident. There are a lot of moving pieces and we want to make sure we get this right rather than rush into a solution that creates another group of people who are treated unfairly.
If recovering users means the protocol never recovers its own lost liquidity, we are prepared for that. Removing the protocol from the recovery equation also makes what we are trying to achieve significantly more realistic.
We’re sorry that our community has had to go through this, even though the vulnerability itself was outside of ZealousSwap. Right now, what matters to us is what we do next.
Thank you again for sticking with us. ❤️
We’ll share the recovery plan as soon as we’re confident it is the fairest path forward.
9
31
131
6,265
Ashton retweeted

dotk 2.0.0 is here!
It brings subnames as well as the first open-source release of the sdks. 👇
Subnames can be created by a name holder (for free), like other records they can be updated on the name page.
They are one way (safety/security): name -> addr.

8
33
95
1,940
Ashton retweeted
This onchain message below is an official communication from Igra Labs regarding the KRC-20 incident on 20 September.
Read and verify the message: explorer.igralabs.com/tx/0x6…
Full text: "To the controller of 0x1B4B7108a49F028598c5ED49B7951c80d44e7FD2 and kaspa:qzfkfuhlswdpemz6qe82squt973kjawx9jax5rn6zrln2533trp0j44cuf43u.
We are contacting you regarding the KRC-20 incident of 20 September 2026. We are seeking the full return of the assets obtained through it, including the iKAS now held at 0x9cc770e5b30f8179ddca2d8dd3d73548829af546 and 0x17030b7ea819a8742f6cec5114733267f14140ab.
Exchange-linked funding of this operation has been identified.
Return the funds to 0xB3300fcC2F3EF3DeCdF8B1f710c21666f33Cbf18 on Igra (chain ID 38833), or contact team@igralabs.com within 72 hours of this transaction's block timestamp to coordinate the return."
13
38
114
16,597
Ashton retweeted
just a gentle reminder that krc20 is not kaspa L1, it only travels over L1 txs as data carriers, but the interpretation of krc20 state is done purely offchain just like any other non-zk based solution. this is why covenants were developed for kaspa L1 with kcc20 built on top of them for native assets (note: kcc20 spec is still in draft)
36
266
819
49,560
Ashton retweeted
Yes. Incident is contained on offfchain indexer, has nothing to do with L1 infrastructure. Apologies for not being clear on this.

just a gentle reminder that krc20 is not kaspa L1, it only travels over L1 txs as data carriers, but the interpretation of krc20 state is done purely offchain just like any other non-zk based solution. this is why covenants were developed for kaspa L1 with kcc20 built on top of them for native assets (note: kcc20 spec is still in draft)
12
33
177
6,831
Ashton retweeted
🚨 KRC 20 Indexer Signature Bypass: Incident Report
We have completed our analysis of the KRC 20 incident that affected ZEAL and other bridged assets.
Importantly, our investigation found no exploit in ZealousSwap, Igra, or Kaspa L1. All three operated as intended. The vulnerability was in the Kasplex KRC 20 indexer.
The report covers the signature bypass, how unauthorized KRC 20 balances were created, how they were bridged to L2, and the resulting impact on liquidity.
Full incident report in the reply.
11
45
130
15,839