
Security Consultant @semperistech . Independent Security Researcher. Cyclist & Scubadiver. MSRC MVR 2022. "So di non sapere"
- Tweets 1,858
- Following 324
- Followers 9,421
- Likes 1,582




Andrea P retweeted

In July, Microsoft fixed CVE-2026-50343, a Windows privilege escalation bug reported by Calif and 9 others, dubbed “Dark Elevator”.
But was it really fixed?
Ask @tiraniddo
projectzero.google/2026/09/w…
3
46
212
16,942


Andrea P retweeted

Been digging deep into the Windows Endpoint Security Platform (WESP) in Win11 25H2, definitely one of the most fascinating security features Microsoft has built in a while.
The concept is neat: compile rules to decision graphs in user mode, hand them to wesp.sys, and let the kernel evaluate them in-path while telemetry streams asynchronously in the background.
I did an AI-assisted reverse engineering dive into the whole stack (wesp.sys, espclient.dll, and wesp_elam.sys), documented the wire protocols, disposition tables, and the enforcement gate, and built esptool, a research harness with 118 XML rule docs so anyone can test live telemetry and in-kernel blocking.
Repo: github.com/marcosd4h/wesp_re…
Tech doc: github.com/marcosd4h/wesp-re…
Thanks to @yarden_shafir for putting this on my radar
1
61
182
13,466

La compromissione dei dati di @Revolut sembra essere molto, ma MOLTO più grave di quanto raccontato.
Se le affermazoni dell'attaccante sono corrette, Revolut non è stata "bucata", ma ha risposto ad una PEC (compromessa dall'attaccante) direttamente delle Forze dell'Ordine, a una richiesta di informazioni.
Cosa che è TENUTA a fare.
Questo significa che ci aspettiamo dal @Viminale che confermi o smentisca, perché se la compromissione riguarda mail legittime (PEC), il problema NON È LIMITATO A REVOLUT ed è ORDINI DI MAGNITUDO più grande e pericoloso.
E può coinvolgere OGNI SERVIZIO e OGNI DATO.
La compromissione qui non è di @Revolut, è di una (o più) Forze dell'Ordine Italiane.

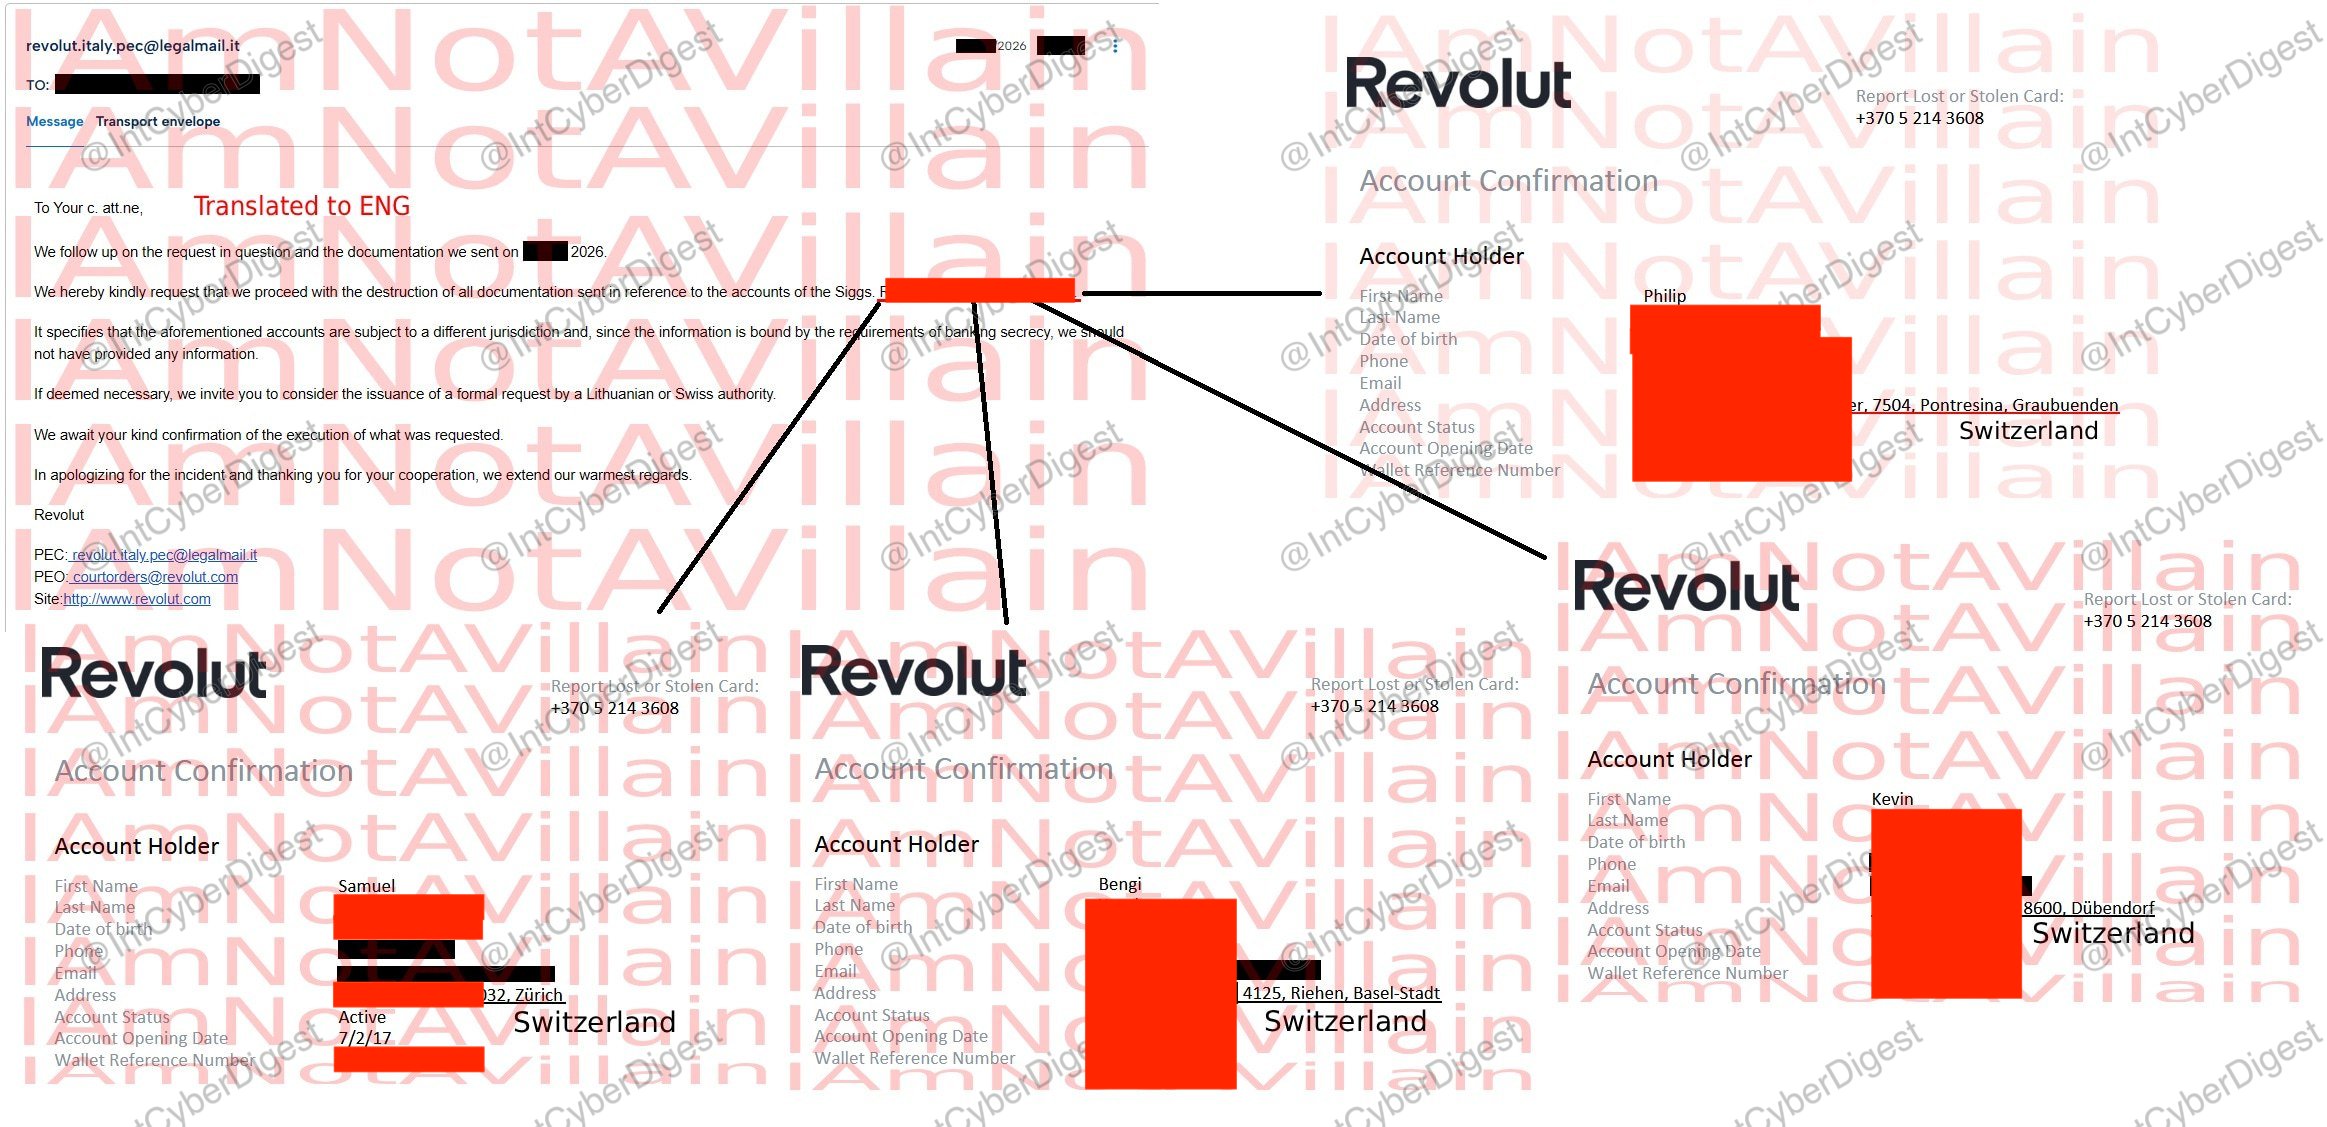
‼️ BREAKING: We're in contact with the Revolut hacker. According to them, they didn't only take Revolut data, they've also compromised multiple Italian law enforcement departments.
They say the operation targeting Revolut ran for six months, and that they used Italian law enforcement systems to send data requests to Revolut.
They claim to hold 147 GB taken from the Italian side, including internal docs, calendars and personal material, among it the chat logs of a federal officer arguing with his wife.



95
507
2,568
248,777
AI may eventually become the new Cold War: everyone keeps building more powerful systems because they can’t afford to let the other side get ahead. Chip manufacturers may become the equivalent of uranium supplier controlling access to the resource that makes the race possible
4
695
Andrea P retweeted

askWAM - Requests Microsoft Entra access tokens silently through Windows Web Account Manager (WAM) by @_dirkjan
github.com/dirkjanm/askWAM
28
95
7,871


Weekend project: I added IAKerb support to Rubeus. My god, this is going to open the floodgates.
Phase 2 of Microsoft's NTLM deprecation is targeted for H2 2026. IAKerb ships for Server 2025 / Win11 24H2 and is already on by default in the June Canary preview. It proxies Kerberos auth through exposed services via SSPI when a client can't directly reach a KDC.
Which means anonymous user enum via AP-REQs with no preauth (zero telemetry), kerberoasting over the open internet, Entra lateral movement through AZUREADSSO tickets and more. All against public facing services.
Blog post soon with potential abuse vectors.

7
93
378
19,824
I have looked at it. When a machine is domain or Entra joined, the Kerberos SSP ignores LocalKDC. So I've not bothered looking into it beyond that as it would be limited to consumer/unjoined scenarios only.
1
2
918

It's 2026.
You should not be onboarding apps that still use Kerberos and NTLM.
You should be actively looking to migrate them to modern authentication.
I hope that's something all of us in cyber can agree on.
20
10
176
11,435

A PoC/exploit has been discovered for vulnerability CVE-2026-26119
Vendor: Microsoft
Product: Windows Admin Center
Description: Improper authentication in Windows Admin Center allows an authorized attacker to elevate privileges over a network.
Link: github.com/r3vpwnx/cve-2026-…
#dbugs_vuln
1
16
87
7,893
Just to be clear, this is NOT a PoC for CVE-2026-26119. It’s a nice python script that authenticates and calls WAC REST endpoints to perform code execution. You could achieve the same thing directly through the web interface. semperis.com/blog/what-you-n…
4
382

Teniamoci stretta la fortuna di essere cresciuti con Guccini, De André, De Gregori, Battiato, Ivan Graziani, la Pfm, Pino Daniele, Ivano Fossati, Edoardo Bennato. E poi ancora con i Pink Floyd, i Led Zeppelin, i Genesis, David Bowie, Queen, U2, Prince e chissà quanti ne dimentico
144
208
1,681
23,082
Super cool research from my colleague Shai Laron on new attack paths to Active Directory that can lead to full domain takeover 😜 . It was presented at Black Hat and he will be speaking again at DEF CON this weekend.
Don't miss this 💪 :
semperis.com/blog/identity-c…
1
77
219
10,629


Ask any pentester who worked internal Hacktive Directory engagements how much we love nested groups and how many indirect admins they create. Or, just run PingCastle as Domain Admin

For the longest time Azure AD/Entra ID didn't support nesting.
In fact M365 Groups still don't support nesting.
There were many enteprise orgs that refused to deploy Entra ID without nesting so finally Microsoft relented and added nesting to just security groups so they could be synced from on-prem and bring the structures over.
However from a security perspective Entra ID still does not support nested groups in a number of scenarios the key one being to grant permissions to apps in Entra. If you assign a group with nested groups to an app, just users that are directly assigned to the group are granted access. Users inside nested groups are ignored.
Adding support for nested groups is one of the #1 requests from many orgs. Hopefully they never allow it.
4
1
40
3,544
